Permissions
Assigning requests to an accountable owner
Set clear rules for request routing, named responsibility, reassignment and cover when an owner is unavailable.
Section
Permissions
Set clear rules for request routing, named responsibility, reassignment and cover when an owner is unavailable.
Permissions
Choosing what a customer should be able to see: a practical guide to the key decisions and checks.
Permissions
Map app tasks to API permissions, distinguish user and unattended access, protect credentials and check that excess actions are denied.
Permissions
Plan who can open a no-code app, see records, change data and maintain it. Map each grant, then check the configured data route.
Permissions
Cross-customer access is a portal failure even if it occurs only through a guessed address or export.
Permissions
Define team or customer record ownership, choose an enforcement point and check access after reassignment.
Permissions
Use a release brief, evidence table and decision record to review staff-built apps before colleagues rely on them.
Permissions
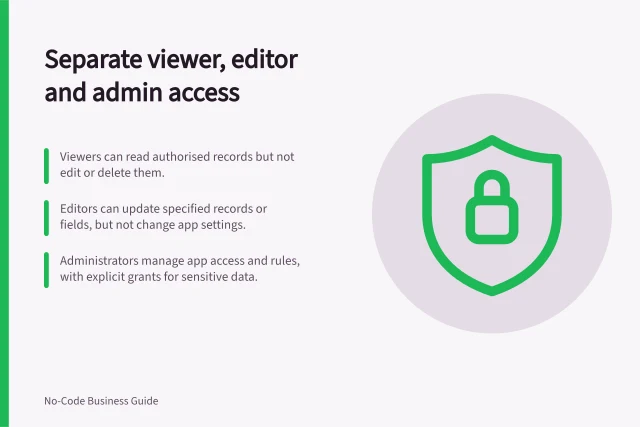
Define what viewers, editors and administrators may do in a no-code app, then match those duties to app and data-source permissions.
Permissions
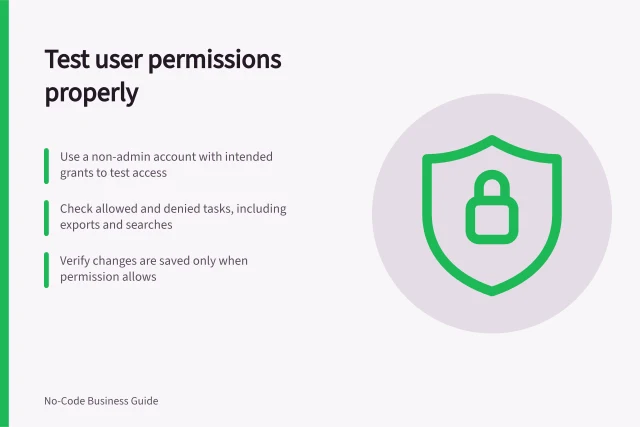
Check permitted and denied actions using an ordinary no-code app account, fictional records and the actual data route.
Permissions
Closing a customer account should end the access it no longer justifies, including old sessions, shared links and downloadable files.